“Is my device listening to me?” is no longer a question reserved for people concerned about hidden microphones or sophisticated espionage. Microphones, voice assistants, artificial intelligence, and audio-processing features are now built into devices that people routinely carry into boardrooms, government offices, private residences, and sensitive meetings.
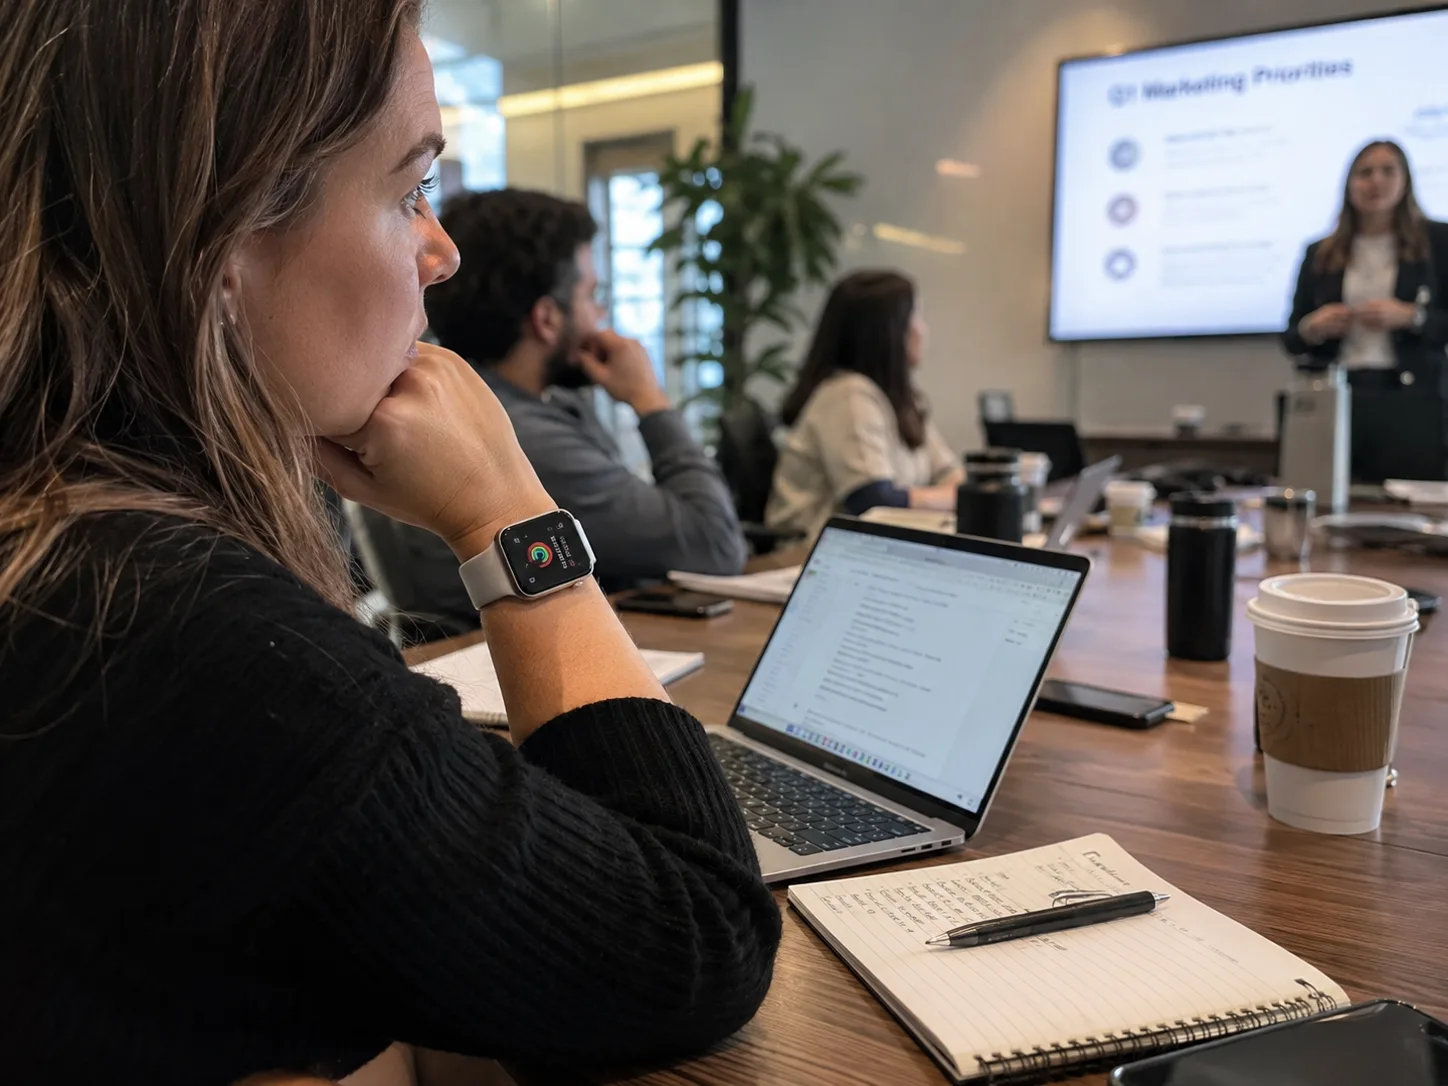
Apple recently announced new Audio Intelligence capabilities for Apple Watch Series 12 and Apple Watch Ultra 4. These include Sound Recognition, Live Rewind, and Siri Recap. When enabled, these features can process surrounding audio, retrieve a text representation of a recent portion of a conversation, or generate summaries and key points from conversations.
Availability
As of October 26, 2026, Apple lists Live Rewind and Siri Recap for beta availability later in 2026. Availability depends on compatible devices and supported regions. Source: Apple Support
Apple states that these features do not create or store an audio recording. According to the company, raw audio is processed in a hardware-isolated environment and then deleted. Live Rewind also produces an audible chime and visual notification when activated. However, the watch may still produce and retain text snippets or conversation summaries when the appropriate features are enabled.
This distinction is important. Listening, recording, processing, summarizing, storing, and transmitting are not necessarily the same thing. From a security perspective, however, all of them must be considered whenever sensitive information is being discussed.
Is My Apple Watch Listening to Me?
The most accurate answer is: it depends on the device, its settings, the features enabled, and how the word “listening” is being used.
Many consumer devices already monitor audio for limited purposes, such as detecting a wake phrase, identifying specific sounds, supporting accessibility features, or responding to voice commands. Apple’s newly announced Audio Intelligence features expand the ways an Apple Watch can process ambient conversations when those features are enabled.
That does not mean every Apple Watch is secretly recording and uploading every conversation. Apple has specifically stated that its new features do not store raw audio recordings. Nevertheless, a device can process spoken information and create a useful text output without preserving the original audio file.
For an individual consumer, the built-in privacy protections may provide meaningful reassurance. For an organization protecting classified, privileged, proprietary, or otherwise sensitive information, the analysis must go further.
The relevant question is not simply, “Is this device recording?” It is, “Can this device capture, process, summarize, retain, or disclose information discussed in this environment?”
Why Wearable Technology Changes the TSCM Conversation
Technical Surveillance Countermeasures, commonly known as TSCM, is often described as the process of locating hidden cameras, microphones, tracking devices, and unauthorized transmitters. That remains an important part of the discipline, but modern TSCM must address far more than traditional electronic bugs.
A smartwatch is not concealed in a wall or disguised as an ordinary office object. It may be openly worn by an employee, visitor, executive, contractor, or member of a protective detail. Because the device is familiar and authorized, it may never be treated as a potential information-security concern.
It also may not behave like a traditional surveillance device. A conventional listening device may continuously transmit audio using a detectable radio-frequency signal. A modern wearable may process information locally, create a text summary, synchronize at a later time, or communicate through ordinary Bluetooth, Wi-Fi, or cellular connections. Its activity may blend into an environment already filled with legitimate electronic devices.
This means radio-frequency analysis by itself cannot answer every security question. A professional TSCM program must combine technical inspection with physical security, device governance, access control, operational awareness, and clear policies for sensitive spaces.
Accidental Information Loss Can Be Just as Damaging
Not every information leak is intentional.
An employee may enter a meeting without realizing that a feature is enabled. A visitor may be unfamiliar with the capabilities of a recently purchased watch. An executive may believe that prohibiting smartphones is sufficient while allowing smartwatches, wireless earbuds, tablets, and other connected devices into the same room.
The resulting exposure can still be serious. A conversation summary involving a merger, legal strategy, government matter, executive movement, product launch, security vulnerability, diplomatic issue, or high-net-worth family could be valuable even without a word-for-word audio recording.
Intent does not determine the damage. Sensitive information that leaves a controlled environment through convenience, misunderstanding, or an outdated policy can create the same operational, financial, legal, and reputational consequences as deliberate collection.
Can a TSCM Sweep Detect an Apple Watch?
A TSCM assessment may identify wireless activity, unauthorized electronics, suspicious transmissions, physical surveillance devices, and vulnerabilities within a protected environment. However, a legitimate wearable does not automatically present as a hostile device.
If a watch is processing audio locally or communicating through an expected connection, traditional detection methods may not establish what information it captured or why it was present. TSCM technicians also cannot determine a person’s intent based solely on the presence of a consumer device.
That is why effective TSCM should not be reduced to a one-time “bug sweep.” The objective is to understand the entire information environment: what must be protected, who has access, which devices are permitted, how those devices operate, where information could escape, and which controls are appropriate for the level of risk.
How Should Organizations Protect Sensitive Conversations?
Organizations should first identify which rooms, meetings, and activities require enhanced protection. Not every workplace needs to be entirely device-free, but sensitive spaces should have written and enforceable rules covering smartphones, smartwatches, earbuds, tablets, laptops, and other microphone-equipped technology.
For higher-risk discussions, the most dependable control is physical separation. Devices can be secured outside the protected area in appropriate storage rather than relying entirely on software settings, airplane mode, or verbal assurances.
Visitor procedures, employee training, meeting classifications, device inventories, technical inspections, and incident-response plans should support that policy. Organizations should also review their TSCM procedures whenever new consumer technology changes how audio, images, location data, or conversations can be processed.
A security policy written only for smartphones may already be obsolete.
Modern TSCM Requires a Holistic Approach
The arrival of AI-enabled, always-listening wearable technology does not mean every smartwatch is an espionage device. It does mean organizations can no longer define surveillance risk solely as a hidden transmitter placed by a hostile actor.
Samaritan Protective Services provides professional TSCM services globally, using advanced technical equipment and trained, certified technicians with years of operational experience. Samaritan protects government, corporate, and private facilities, personnel, information, and other critical assets from espionage, technical surveillance, and unintended information exposure.
Our intelligence-led approach considers technical threats alongside authorized devices, human behavior, physical access, operating procedures, and the accidental ways sensitive information can leave a protected environment.
If your organization discusses information that could cause harm if disclosed, the right time to evaluate your exposure is before an incident occurs.
Request a confidential TSCM assessment from Samaritan Protective Services to determine whether your facilities, policies, and technical safeguards address the risks created by modern wearable devices.
Request a Confidential TSCM Assessment